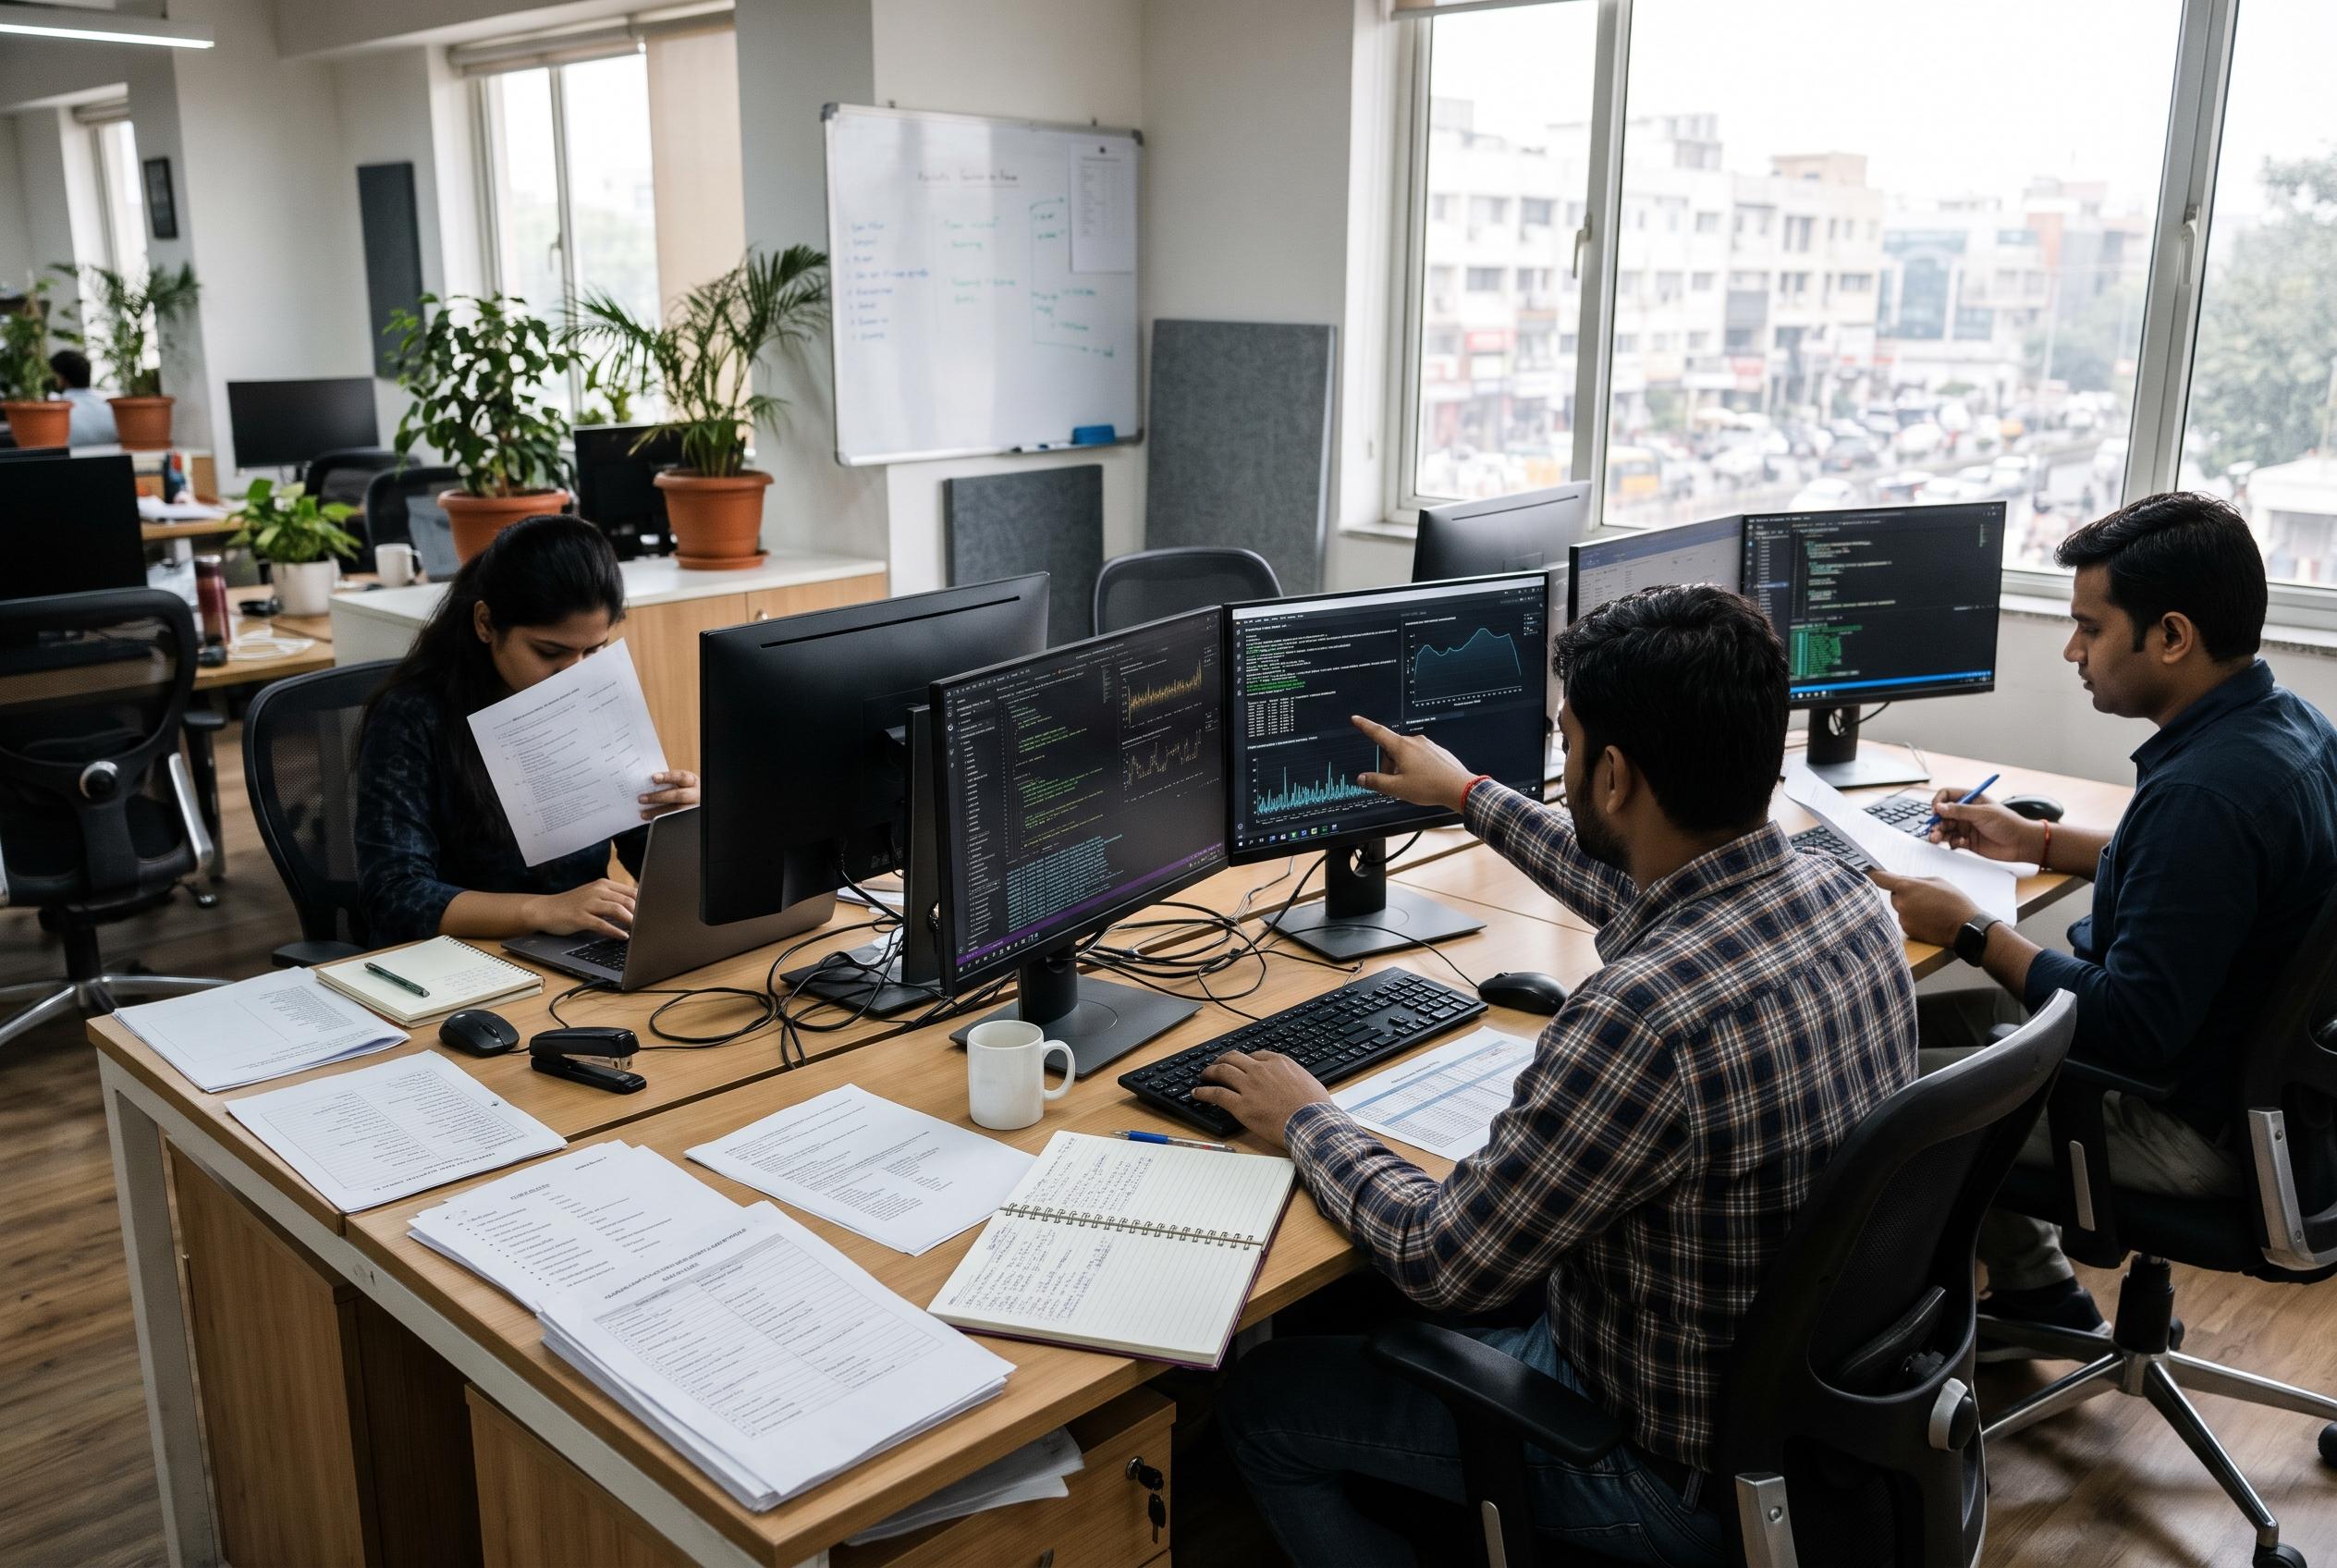
As AI agents gain the ability to use software, remember past tasks and hand work to other agents, India’s CERT-In is calling for sharper security audits. The guidelines focus on practical risks such as unauthorised tool use, excessive permissions and runaway delegation, giving organisations a clearer checklist for keeping increasingly independent AI systems under control.
AI agents are being asked to prove they know their limits
An AI agent that can open tools, run code or assign tasks to another system is a different proposition from a chatbot that simply answers a question. That extra autonomy can be useful, but it also creates more ways for an action to go wrong before a person spots it.
CERT-In’s AI security auditing framework calls for tests that probe those boundaries directly. Auditors should check whether an agent can bypass an approval step, act beyond its authorised permissions, or use credentials in an unintended way, according to the guidelines.
Memory and delegation deserve a closer look
An agent’s memory can make it more useful across tasks, but it can also preserve information that shouldn’t stick around. The framework calls for testing whether stored information can be manipulated, whether one user’s data can surface to another, and whether sensitive details are kept or reused without permission.
Delegation adds another layer. When an agent passes work to another agent, the handoff needs clear limits and oversight; otherwise, a simple task can become a chain of actions that’s difficult to track. The UK National Cyber Security Centre has also highlighted the importance of managing cyber risks associated with agentic AI.
Multi-agent systems need clear identities and brakes
For systems where several agents cooperate, CERT-In says each one should have a distinct identity and clearly defined permissions. Their communications should be authenticated and logged, so an organisation can work out which agent made a request and whether it was allowed.
The framework also calls for safeguards against repeated handoffs, uncontrolled task creation and loops in which agents keep assigning work to one another. For higher-risk systems, organisations should be able to stop an individual agent or an entire workflow and revoke access credentials.
Good audit records make failures easier to untangle
A useful audit trail should capture what agents asked of one another, which tasks they delegated, what permissions they used and which tools or external actions were involved. Those records can help an organisation reconstruct how an outcome happened, rather than relying on a vague summary after the fact.
CERT-In also calls for an inventory of production AI components, including models, training data, software and external tools. If a third-party provider doesn’t disclose internal details, organisations should document the information gap and explain how it affects the audit.
Human oversight still matters, especially in audits
AI can help auditors review information, but the guidelines say AI-generated summaries can’t replace evidence or professional judgement. Auditors who use AI should independently verify its outputs, a sensible reminder that a polished answer isn’t the same as a proven one.
The broader message is practical: the more freedom an AI system has to act, the more clearly its access, decisions and emergency stops need to be tested. For organisations adopting agentic AI, that kind of preparation may be less glamorous than a new feature, but it’s what helps keep the feature useful.
A capable agent should be easy to trace, limit and stop when needed.
Disclaimer: This article may have been created with AI assistance and reviewed by our editorial team. It is provided for general informational purposes only. Readers should verify information independently before relying on this content.