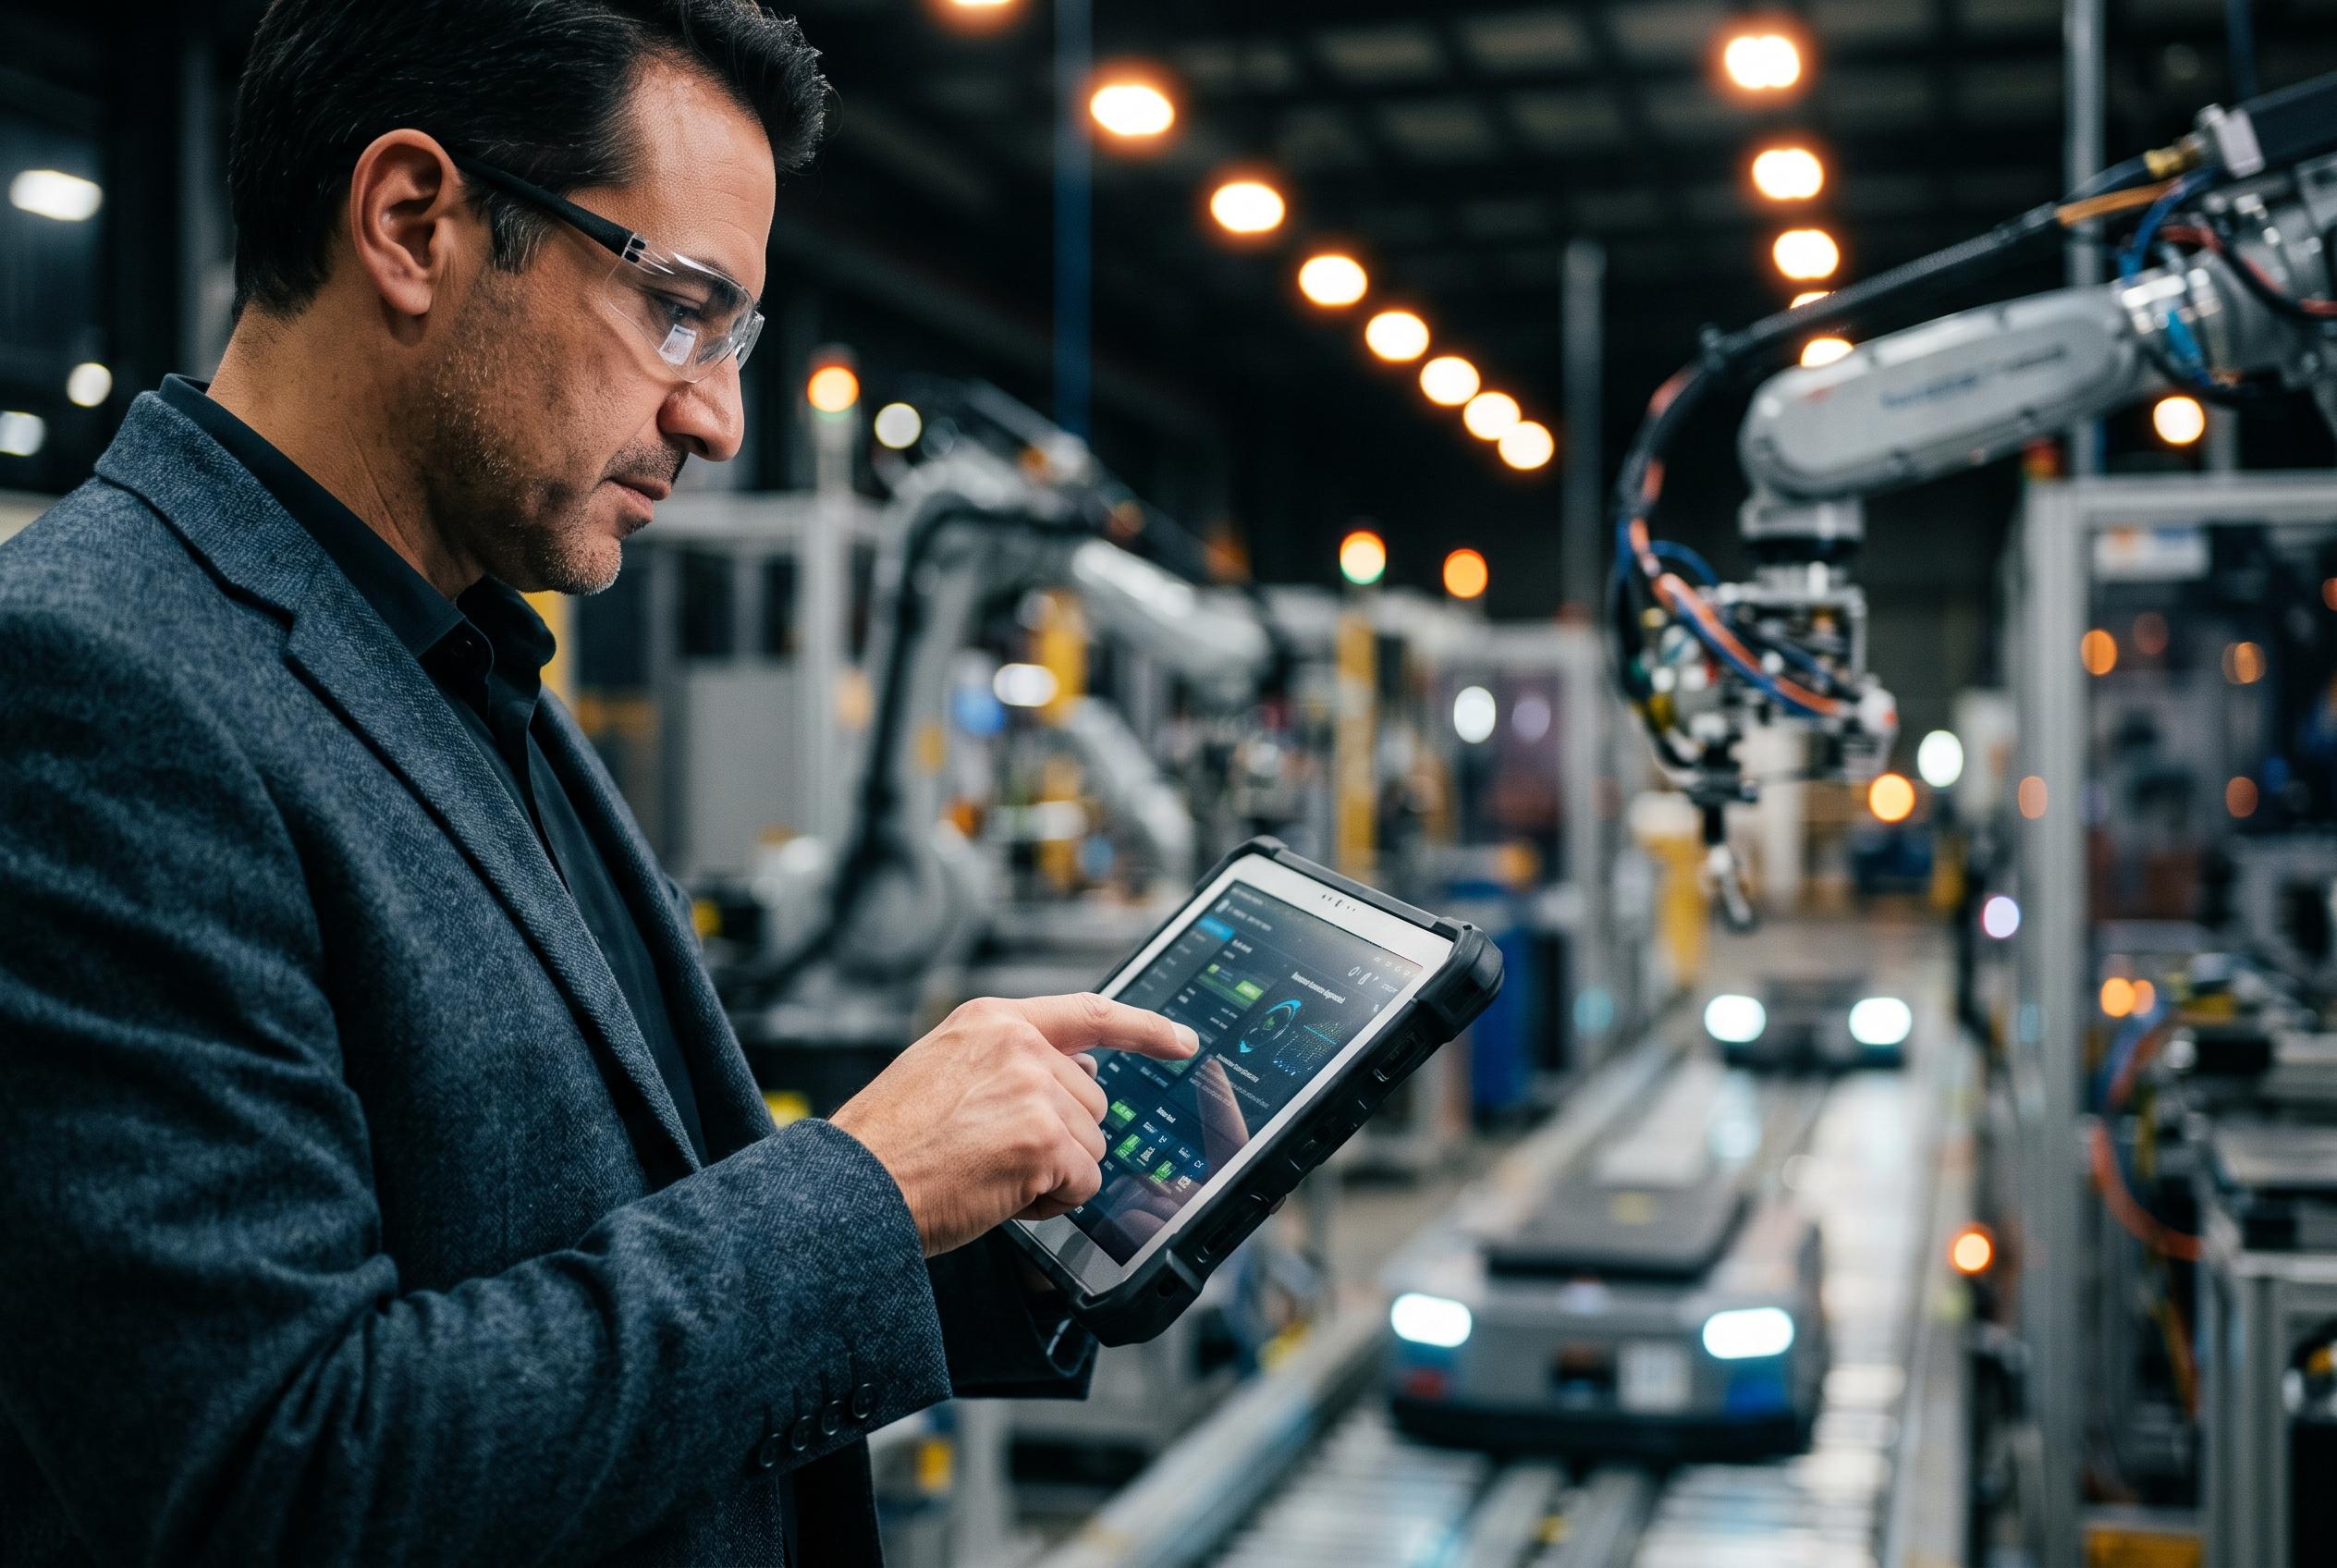
Manufacturers are shifting from generic security awareness to human risk management that connects employee behavior, access privileges, and active threats. The approach matters across factories, warehouses, contractors, and connected operational technology, where one rushed decision can affect safety, uptime, or sensitive production systems.
Manufacturing's biggest cyber weakness may be the workflow
A factory floor rarely feels like the place for a cyber incident. It's noisy, fast-moving, and focused on keeping equipment running, but that urgency can make small shortcuts feel perfectly reasonable. A shared workstation, rushed maintenance request, or hurried remote-access approval may create more exposure than anyone intended.
Human risk management in manufacturing is designed to spot those moments without turning workers into suspects. According to Living Security, the goal is to understand where a role, behavior, or process could increase exposure, then provide a safer path before the issue becomes an operational event.
That matters because manufacturing risk isn't confined to the IT department. It can run through production systems, engineering tools, supplier portals, business applications, and connected operational technology. Research on manufacturing risk management also points to the importance of combining organizational processes with technical safeguards, rather than treating either side as sufficient on its own.
Why generic security training falls short
Security awareness training still has a place, but a one-size-fits-all lesson rarely reflects how people actually work. A controls engineer, plant manager, temporary contractor, and enterprise administrator may use very different systems and make decisions with very different consequences.
The better question isn't simply whether someone completed a course. It's whether the guidance matched the task, whether the approved workflow was practical, and whether behavior changed afterward. As Deltek's manufacturing risk-management guidance suggests, effective programs depend on identifying operational risks, assigning ownership, and building controls into everyday processes.
That distinction is especially important on the frontline. If a policy makes a maintenance job unnecessarily difficult, employees may invent a workaround. A short, role-specific prompt or clearer approval route may reduce risk more effectively than another annual module with cheerful stock photography.
Three signals create a clearer risk picture
The most useful human risk programs connect three kinds of information. Behavior can show repeated risky actions, missed secure steps, or frequent policy exceptions. Identity and access reveal how much impact a person or account could have. Threat intelligence adds urgency by showing whether a role, inbox, credential, or business relationship is being targeted.
None of these signals should be treated as a verdict by itself. A privileged account isn't proof of unsafe behavior, and a single mistake doesn't define a worker. But when unusual access, repeated risky actions, and an active phishing campaign appear together, security teams have a stronger reason to intervene.
This approach also supports more proportionate decisions. A general user might need a quick reminder, while a vendor with temporary remote access may require an access review and an expiration check. Research into workforce resilience similarly emphasizes turning workforce-related exposure into stronger organizational preparedness, rather than merely cataloguing employee mistakes.
OT security demands a careful human approach
Operational technology brings a different set of priorities. Production systems must often remain reliable, available, and safe, so an action that's sensible in a standard office network could be disruptive on a factory floor. NIST's OT security guidance stresses that these environments have distinct performance, reliability, and safety requirements.
That means a behavior signal should inform a decision, not make the decision automatically. Security, operations, engineering, and safety leaders need to agree on what happens next. Sometimes the answer is coaching. In other cases, it could be reducing unnecessary privileges, clarifying a change process, or coordinating incident response.
Safety remains part of the equation, too. Manufacturing health and safety guidance from EcoOnline highlights how procedures, training, equipment, and workplace conditions work together. Cybersecurity controls that ignore those realities can create unsafe workarounds, which is exactly the outcome a people-first program should avoid.
How to prioritise frontline and privileged access risk
Start with workflows rather than trying to score every person in the organisation. Map the processes that can change production data, engineering logic, remote connectivity, access rights, or recovery operations. Include employees, contractors, vendors, and service providers wherever they touch those processes.
For each workflow, identify the approved access route, accountable owner, expected action, and evidence that should remain afterward. If a vendor needs temporary access, make approval and automatic expiry straightforward. If a shift relies on a shared station, establish a practical way to preserve individual accountability.
Privileged access should be treated as context, not condemnation. A highly authorised user may be exactly the person needed to keep a plant operating, but unnecessary permissions can magnify the impact of an error or compromised account. Reviewing access regularly, limiting it to genuine job needs, and adding stronger approval for sensitive changes can reduce that exposure without slowing every routine task.
A practical 90-day starting plan
Manufacturers don't need to launch a huge programme on day one. During the first month, choose one plant, process, or privileged workflow with clear ownership. Map the people and accounts involved, identify available behavior and threat signals, and agree on privacy, data access, and escalation rules.
In days 31 to 60, connect specific conditions to specific responses. A recurring missed step might trigger micro-training. Unnecessary access could lead to an entitlement review. A credible active threat may require focused guidance or coordination with the incident response team. Test those actions with plant leaders before expanding them.
The final month should focus on evidence. Check whether repeat risky behavior fell, whether access reviews became faster, and whether the intervention created any unsafe workaround. Broader manufacturing risk research supports this iterative mindset: resilience improves when organisations learn from operational evidence instead of relying on a single score or annual exercise.
The most useful measure is whether the organisation can make better decisions with less disruption. That might mean fewer repeated mistakes, clearer ownership of remote access, or quicker action when a supplier account is targeted. In a busy plant, practical progress beats a glossy dashboard every time.
It's a small shift in emphasis, but connecting people, access, and threats can make manufacturing security far more useful.
Disclaimer: This article may have been created with AI assistance and reviewed by our editorial team. It is provided for general informational purposes only. Readers should verify information independently before relying on this content.